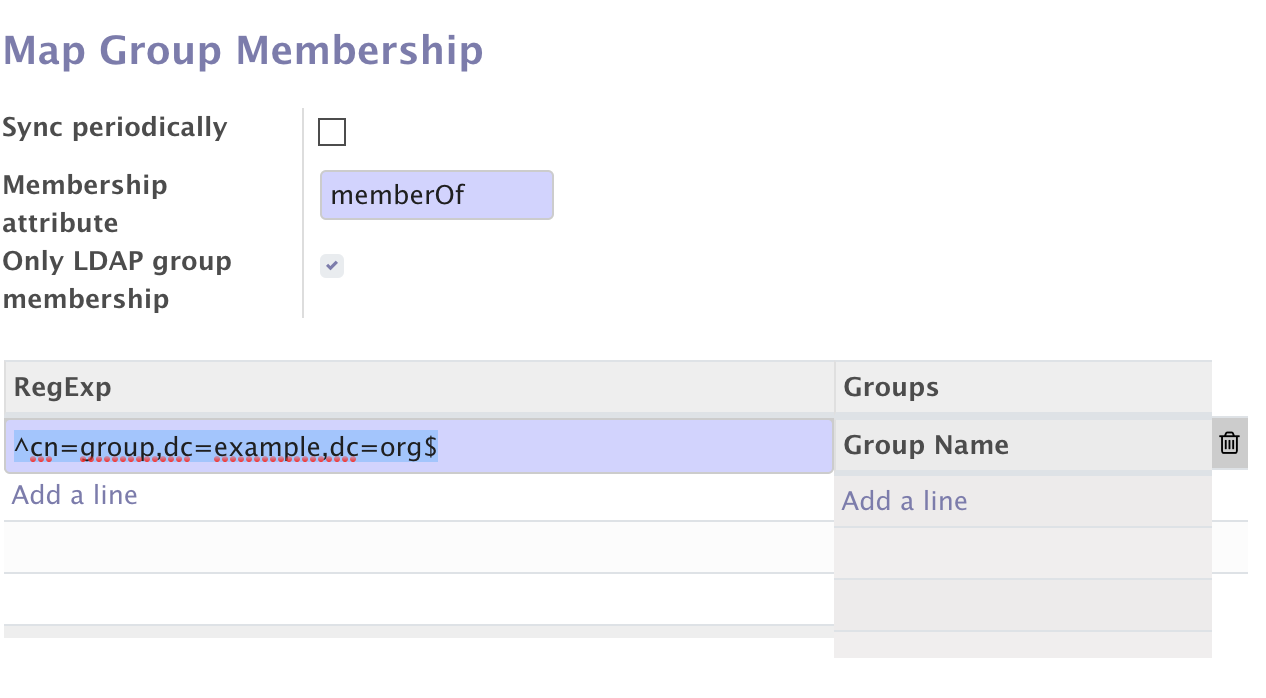
[12.0][ADD] auth_ldap_group_sync: alternative to users_ldap_groups - #52
alexey-pelykh wants to merge 1 commit into
Conversation
 alexey-pelykh
commented
Nov 7, 2018
332955b to
d5a1476
Compare
|
@nikul-serpentcs @hbrunn @dreispt I'd like to kindly ask for a review of this PR |
d5a1476 to
916b30e
Compare
|
@nikul-serpentcs Thanks! Ready for re-review |
|
Since this seems to be proposing an alternative implementation to an existing feature, it begs the question:
|
|
@dreispt This module would be preferred in case Odoo permissions replicate LDAP group membership of single LDAP group granting multiple permissions in Odoo, with I did an attempt to add these features in #46 yet reverted ti just-migration as original module lost its simplicity and flexibility or would become unmaintainable due to lots of if/else to support original behavior. |
|
you can have both: Add a computed field to the original module that reads the original field and maps it to your simplified configuration and the inverse. Then declare a group that you use to restrict a view override which replaces the original field with the computed field. So just by adding/removing a user to/from the group, you can switch which field is shown. Make your group a standard implied group of base.group_user, and give the possibility to turn that off, something like 'show advanced configuration'. |
|
@hbrunn thanks for the suggestion! Adding this feature to original module was my original approach and in the end it proved itself to be overcomplicating the original codebase. Making an extra module that workarounds its purpose in order to be an extension of another module has no value IMHO. Thus if end-user needs LDAP-group-based permission management, there's one module, while advanced LDAP-attribute-based permission management there's another module. |
|
Some thoughts: From a functional PoV, I can see this as a friendly UI over In an ideal world this module would wrap the |
|
Good point, I'd suggest to describe use-cases for both modules in readme. From code and functional perspective it would be hard to reuse |
916b30e to
5d02013
Compare
Syncing from upstream OCA/server-auth (11.0)